
01
What agentic AI in a CRM actually is
Most AI in a CRM until recently was a copilot: it suggested, summarized, and drafted, and a human did every actual write. Agentic AI is different in one specific way. It plans a sequence of steps and executes them against the system on its own, deciding what to do next based on what it finds. Ask a copilot to update a deal and it drafts a note for you to paste. Give an agent the same job and it reads the call transcript, decides which fields changed, writes them, creates the follow-up task, and opens the renewal opportunity, without a click between steps. That autonomy is the entire point and the entire risk. Salesforce now markets Agentforce as an agentic layer, Microsoft has agents in Dynamics 365, and HubSpot and Zoho have shipped their own. The category is real and arriving fast. The question this article answers is the one every RevOps lead is actually asking: how do you let it write to the CRM without wrecking the data your forecast runs on.
02
What agents are already doing in CRMs
Strip away the marketing and the useful agentic CRM work is a short, concrete list. Inbound enrichment and routing: an agent takes a form fill, enriches the record, matches it against existing accounts, scores it, and assigns an owner in seconds instead of the twenty minutes that lets a lead go cold. Post-call updates: it turns a call transcript into an updated stage, next step, and qualification fields, plus the follow-up task and email. CRM hygiene: it dedupes and merges records, enforces required fields at each stage, and captures activity automatically. Retention: it watches usage and support signals and flags a renewal risk before the CSM would have seen it. Notice the pattern. Every one of these is a trigger, a data join across systems, a decision, a write, and ideally a verification. The write is where the value lands and where the danger lives, because a CRM is not a scratchpad, it is the system your forecast, your routing, and your comp plan all read from.
03
The real failure mode: corrupting the pipeline
The number that should set the stakes: in Validity's 2025 State of CRM Data Management report, 76 percent of organizations said less than half of their CRM data is accurate and complete, 37 percent said they lost revenue directly because of data quality, and companies reported losing an average of 16 deals a quarter to unreliable data. Gartner, cited by ZoomInfo, puts the cost of poor data quality at an average of 12.9 million dollars a year. Now hand an autonomous agent write access to that system. The failure modes RevOps teams report are specific and repeatable: an agent edits an opportunity stage or amount off a misread signal, it creates duplicate records because it did not check for an existing match, or it overwrites a field nobody standardized. A single confused run does not make one mistake, it can propagate that mistake across hundreds of records faster than a human could catch it, and every downstream report inherits the damage. That pipeline corruption is the cost people do not price in when they turn autonomy on.
04
Trust it by gating on consequence, not task
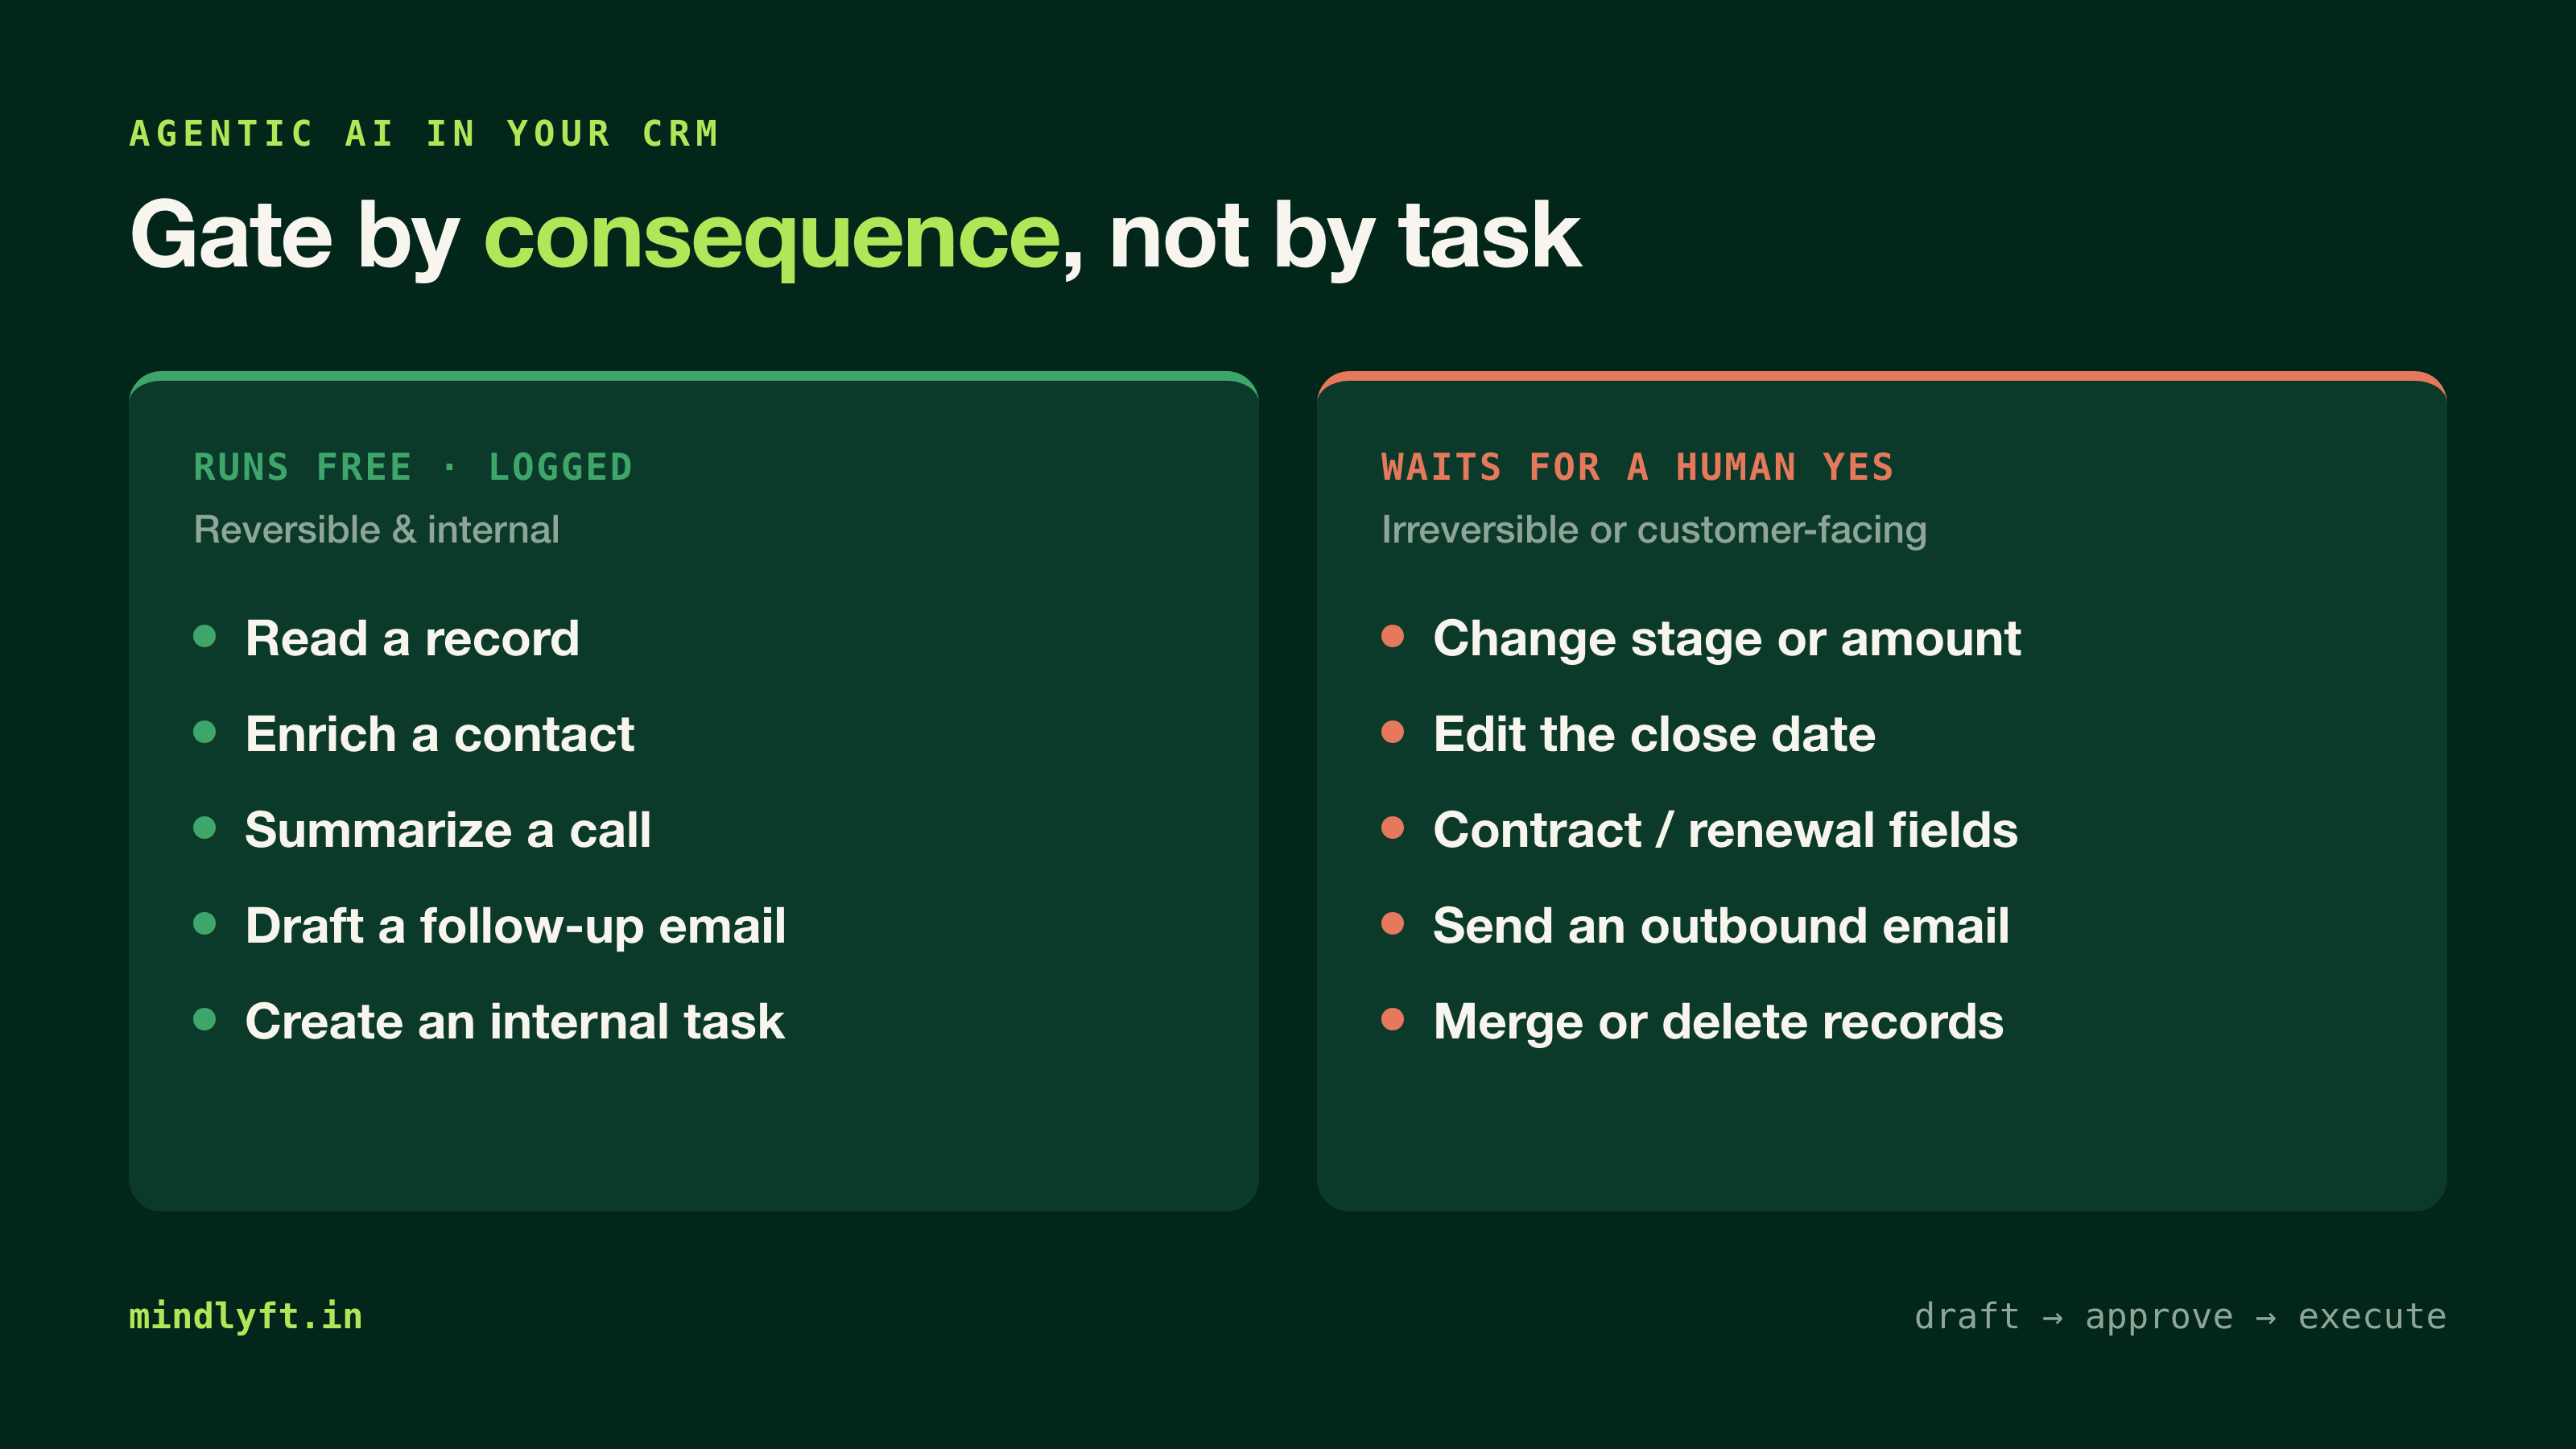
So how do you trust an agent with the CRM. You draw a line, and you draw it around consequence, not around task. Reads and low-risk reversible writes run on their own, logged: pulling a record, enriching a contact, summarizing a call, drafting a follow-up, creating an internal task. Anything that changes a system of record, touches a customer, or is hard to undo waits for a human to approve, edit, or reject before it executes: opportunity stage and amount, close date, contract and renewal fields, an outbound email, and any merge or delete. This is the same instinct Anthropic builds into its own agent tooling, where the agent starts read-only and asks before it modifies anything, and it is what OWASP names in its 2025 LLM top ten as the fix for Excessive Agency, high-impact actions running without confirmation. Put the human on the two or three irreversible calls per workflow and get out of the way on the forty that are not. That is what makes autonomy safe to turn on at all.
05
Give each agent its own identity, scoped
The line only holds if it is enforced in the platform, not in the prompt. A prompt that says do not delete records is a request; an API token without delete scope is a control, and you should assume the instruction will eventually be ignored or manipulated. So give every agent its own identity, never a shared service account and never a human's borrowed login, and scope that identity to the exact objects and fields its job needs. Salesforce's Agentforce works this way by design: each agent runs as its own agent user with its own permission set, and the common mistake its security guidance warns about is scope sprawl, granting broad access early to get it working and never walking it back. The scale of the problem is easy to underestimate. CyberArk's 2025 identity report found machine identities now outnumber human ones by more than 82 to 1, and most organizations still do not treat them as privileged. An agent with its own scoped identity gives you three things a shared login cannot: every write attributed to the agent in the audit trail, the ability to shut off one agent without locking out a person, and permissions you can actually reason about.
06
The duplicate-records problem, specifically
Duplicate records deserve their own answer, because they are the single most reported way agentic CRM writes go wrong and they quietly wreck reporting long before anyone notices. The fix is a pattern borrowed from good data engineering. Have the agent write to a staging state first, a draft field or a pending record, rather than straight to the live object. Run a dedupe and validation pass before anything is promoted: match on email, domain, and fuzzy name, apply survivorship rules to pick the winning values, and only then write to the record of truth. And stamp every write with provenance, which agent made it, off which trigger, from which source. Provenance is the piece almost everyone skips, and it is what lets you mass-revert one agent's bad run in a single operation without touching a single human edit. Without it, a duplicate-spawning run means a manual cleanup and a lingering fear you missed some. With it, the blast radius is bounded by what you can see and undo.
07
The black-box objection: show the diff, keep the trail
There is an objection RevOps leaders raise that is completely fair: if I cannot read the prompt that wrote the message, how do I fix an off-brand send. The answer is not to read the prompt, it is to never let the write be a black box in the first place. Every consequential action the agent proposes should show a diff before it executes: the old value, the new value, and the evidence behind it, such as the call excerpt that justified the change, so a human can approve it in two seconds or catch the one that is wrong. And every action, approved or rejected, lands in an audit trail keyed to the agent's identity. That turns two problems into non-problems. An off-brand send is caught at the diff, before the customer sees it, not discovered in a reply. And when something does slip through, you can see exactly what was written, why, and off what input, instead of guessing at a prompt you cannot inspect. The goal is not a more trustworthy model. It is a workflow where trust is unnecessary because every write is visible and reversible.
08
How is agentic AI in a CRM different from post-call execution?
Agentic AI in a CRM is the broad category, any agent that plans and executes multi-step actions on CRM records rather than just answering questions about them. Post-call execution is one specific, high-value slice of that category: the agent reads a call transcript and turns what was said into the exact CRM writes, tickets, and follow-ups that call implied, an updated stage, a new next step, a drafted recap email, rather than leaving a rep to do that data entry by hand. The distinction matters because agentic CRM tools vary enormously in scope, some only enrich and route inbound leads, others touch renewal risk or dedupe, and post-call execution is the piece most directly tied to what a rep or CSM actually did today. If your CRM agent story starts and ends with enrichment, post-call execution is usually the highest-leverage gap to close next.
09
What does an approval layer for agentic CRM writes actually look like?
In practice it is a queue, not a dashboard. The agent proposes a specific write, an opportunity stage change, a new field value, a follow-up email, and shows the diff: the old value, the new value, and the evidence behind it, such as the call excerpt that justified the change. A named person approves, edits, or rejects it in a click, and the write only reaches the CRM after that decision, logged either way. Mindlyft's approval layer applies this per action rather than per workflow, so routine reads and reversible internal writes can run automatically while anything that touches a customer or a system of record waits for a yes. The design goal is that approving takes less time than the mistake it prevents would take to clean up, otherwise reviewers stop reading and the gate becomes theater.
10
How much does it cost to build safe agentic CRM automation yourself vs buying it?
Building the approval queue, the scoped agent identities, the staging-and-dedupe pipeline, and the audit trail described above is real engineering time, plus the ongoing maintenance every CRM integration needs as fields and workflows change. Run your own numbers, current tooling spend against the engineering hours you would need, against a fully managed option using the GTM cost calculator. Mindlyft builds this as a GTM engineering subscription: the first workflow, including the approval gate, is engineered free, then it is a flat monthly fee, see current pricing or apply for a slot to scope your CRM's first safe write.
11
Does your data support this, and where a subscription fits
One caveat before you turn any of this on: agentic AI does not fix a data problem, it accelerates one. If your enrichment is wrong and your fields are not standardized, an agent will confidently propagate that faster than a human ever could, which is the RevOps way of saying you are just automating garbage. So the honest first step is often not an agent at all, it is the dedupe, the field enforcement, and the validation rules that make the data trustworthy enough to act on. That is unglamorous systems work, and it is exactly what a GTM engineering on subscription partner is for: someone who wires the enrichment, the suppression, the staging-and-dedupe, and the approval gate into your existing CRM, then runs the agent on top of a foundation that can support it. This is how Mindlyft builds. ASTRA drafts the CRM updates, tickets, and follow-ups after a call, writes reversibly with an audit trail, and holds every consequential change in a review queue for a human yes, so autonomy widens only as the record earns it. The first workflow is engineered free, then it is $5,995 per month, at mindlyft.in.
Sources behind this piece
- [01]Validity, The State of CRM Data Management in 2025
- [02]ZoomInfo Pipeline, The Real Cost of Poor Data Quality (Gartner figures)
- [03]Salesforce Ben, How to Secure Agentforce
- [04]OWASP LLM06:2025, Excessive Agency
- [05]CyberArk, Machine identities outnumber humans 82 to 1
- [06]Anthropic, Our Framework for Developing Safe and Trustworthy Agents
- [07]SailPoint, AI Agents: The New Attack Surface (2025 survey)
FAQ
What is agentic AI in a CRM?
Agentic AI in a CRM is software that takes actions on your CRM data rather than just answering questions about it. It plans and executes multi-step work, enriching records, routing leads, updating fields after a call, merging duplicates, and flagging renewal risk, deciding what to do next based on what it finds. That autonomy separates it from a copilot, which only suggests and drafts while a human performs every write.
What can an AI agent actually do in a CRM?
The useful, proven work is a short list: inbound enrichment and lead routing, post-call field and task updates, CRM hygiene such as dedupe, merge, required-field enforcement, and activity capture, and retention signals like renewal-risk flags. Each follows the same shape: a trigger, a data join, a decision, a write, and a verification. Reads and reversible writes are safe to automate; writes that change a system of record or touch a customer should wait for approval.
Can you trust an AI agent to write to your CRM?
Yes, if you gate by consequence rather than trusting the model. Let the agent run reads and reversible, low-risk writes on its own with a log. Require a human to approve anything hard to undo or customer-facing: opportunity stage and amount, close date, contract fields, outbound emails, and merges or deletes. Enforce those limits in the platform's permission layer, not in the prompt, and keep an audit trail so every write is visible and reversible.
How do I stop an AI agent from creating duplicate records?
Have the agent write to a staging state first rather than straight to live records, then run a dedupe and validation pass, matching on email, domain, and fuzzy name and applying survivorship rules, before promoting anything to the record of truth. Stamp every write with provenance (which agent, which trigger, which source) so that if a run does spawn duplicates you can mass-revert that one agent's writes in a single operation without touching human work.
Which CRM actions should always require human approval?
Anything irreversible or customer-facing: opportunity stage and amount changes, close dates, contract and renewal fields, outbound emails, and record merges or deletions. Reads, enrichment, call summaries, internal task creation, and other reversible low-stakes writes can run autonomously once they are fully logged and the agent has a clean track record. Gate by consequence, not by how important the task feels.
Does agentic AI work in Salesforce, HubSpot, and Zoho?
Yes. Salesforce offers Agentforce, Microsoft has agents in Dynamics 365, and HubSpot and Zoho have shipped agentic features, each able to read and write CRM records. The platform differs but the safety requirements do not: give each agent its own scoped identity, gate consequential writes behind human approval, and keep an audit trail, regardless of which CRM you run.
What is the difference between agentic AI in a CRM and RPA?
RPA follows a fixed script, click here, copy this field, paste there, and breaks the moment the screen or process changes. Agentic AI plans dynamically: it reads a call transcript or a record's current state and decides what to update based on content, not a hardcoded sequence of clicks. That flexibility is also the risk, an RPA bot fails loudly when its script breaks, while an agent can confidently execute the wrong decision, which is why approval gates matter more for agentic systems than for traditional RPA.
Do agentic AI features already built into Salesforce or HubSpot need a separate approval layer?
Usually yes, if you want consequential writes gated. Native features like Salesforce Agentforce or HubSpot's agent tools handle the reasoning and the write inside their own platform, but the approval-and-audit layer, who signs off before a customer-facing or system-of-record change goes live, is typically a separate decision you configure yourself, whether that is the platform's own permission settings or a layer added on top across every tool an agent touches.
Want the GTM engineer without the headcount?
Apply for a subscription slot and get unlimited GTM engineering requests handled at a fixed monthly rate.
Apply for a slot